Blog
nginx flaws (CVE-2026-123634 and others): Am I affected and what to do?
nginx fixed ten flaws, including use-after-free in the resolver, in the mail proxy module and in HTTP/3 (CVSS 4.0: 9.2). Fixed are 1.31.9 (mainline) and 1.30.7 (stable), older branches get no separate fix according to nginx.org. Exploitation is not confirmed as far as we know. Here is how to check and what to do.
Published by Stackwatch-Team
Researched and drafted with AI assistance, reviewed and approved by the Stackwatch-Team.
What happened
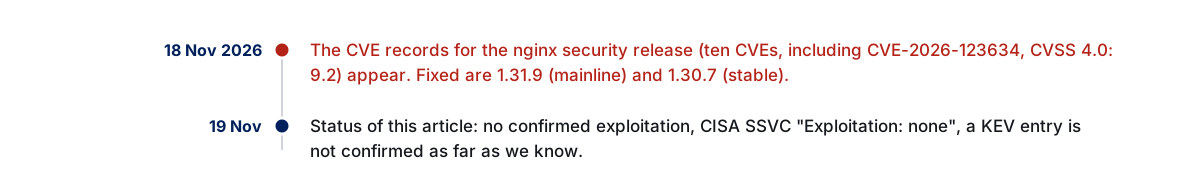
nginx published a security release covering ten CVEs, the CVE records are dated 18 November 2026. Everything is fixed in the open source versions 1.31.9 (mainline) and 1.30.7 (stable). The main flaws according to nginx.org and the vendor's CVE records (CNA F5):
- CVE-2026-123634: use-after-free in the resolver. CVSS 4.0: 9.2 CRITICAL, CVSS 3.1: 8.1 HIGH (
CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H). - CVE-2026-113425: use-after-free in the mail proxy module. CVSS 4.0: 9.2 CRITICAL, CVSS 3.1: 8.1 HIGH.
- CVE-2026-121810: use-after-free in HTTP/3. CVSS 4.0: 9.2 CRITICAL, CVSS 3.1: 8.1 HIGH.
- CVE-2026-118899: infinite loop with TLS 1.3 (denial of service). CVSS 4.0: 8.7 HIGH, CVSS 3.1: 7.5 HIGH.
- CVE-2026-123007 (memory corruption in HTTP/2 flow control) and CVE-2026-123633 (use-after-free in HTTP/2): we have no CVSS value for either, so we do not state one. nginx.org rates 123007 as "major" and 123633 as "medium" (nginx.org scale, not CVSS).
- Plus four minor ones: CVE-2026-120993, CVE-2026-125283, CVE-2026-120967 and CVE-2026-123640.
For CVE-2026-123634 and CVE-2026-113425 the CVE records name code execution as a possible impact if ASLR is disabled or the attacker can bypass ASLR. For CVE-2026-121810 the record says "possibly". According to Cloudflare Radar (secondary source, not confirmed by the vendor) the researcher Xint tracks five of the flaws under the name "nginx2root".
Affected and fixed versions
Fixed are NGINX Open Source 1.31.9 (mainline) and 1.30.7 (stable). Affected according to nginx.org ("Vulnerable"):
| CVE | Affected | Fixed in |
|---|---|---|
| CVE-2026-123634 (resolver) | 0.6.18 to 1.31.8 | 1.30.7, 1.31.9 |
| CVE-2026-113425 (mail proxy) | 0.5.33 to 1.31.8 | 1.30.7, 1.31.9 |
| CVE-2026-121810 (HTTP/3) | 1.25.0 to 1.31.8 | 1.30.7, 1.31.9 |
| CVE-2026-118899 (TLS 1.3) | 1.13.0 to 1.31.8 | 1.30.7, 1.31.9 |
| CVE-2026-123007 (HTTP/2) | 1.9.5 to 1.31.8 | 1.30.7, 1.31.9 |
| CVE-2026-123633 (HTTP/2) | 1.19.7 to 1.31.8 | 1.30.7, 1.31.9 |
| CVE-2026-120993 | 1.31.4 to 1.31.8 | 1.31.9 |
| CVE-2026-125283 | 0.9.6 to 1.31.8 | 1.30.7, 1.31.9 |
| CVE-2026-120967 | 1.25.5 to 1.31.8 | 1.30.7, 1.31.9 |
| CVE-2026-123640 | 1.15.2 to 1.31.8 | 1.30.7, 1.31.9 |
Two notes on the sources. For CVE-2026-118899 the CVE record differs: it lists only 1.30.0 up to before 1.30.7 and 1.31.0 up to before 1.31.9. We follow nginx.org here. The CVE record for CVE-2026-121810 contains "1.25.09", probably meaning 1.25.0.
Older branches such as 1.28 or 1.26 get no separate fix according to nginx.org: the page lists only 1.31.9 and newer as well as 1.30.7 and newer as not vulnerable. If you run an older branch, you have to move to 1.30.7 or 1.31.9. NGINX Plus has its own fixed releases. They are listed in the CVE records and the F5 advisories (K000163925 to K000163935), which we did not evaluate here.
Is it being exploited?
As far as we know: no confirmed exploitation.
- The CISA assessment (SSVC) in the CVE records for CVE-2026-118899, CVE-2026-113425, CVE-2026-121810 and CVE-2026-123634 says "Exploitation: none". We did not read it for CVE-2026-123007 and CVE-2026-123633.
- CISA's Known Exploited Vulnerabilities catalog (KEV) does not list nginx as far as we know. The catalog version we checked (2026.11.17) is older than the publication on 18 November.
- According to Cloudflare Radar (secondary source) the sources reviewed do not report exploitation in the wild, and Xint left out the final exploit steps.
This can change. How to read CVSS, EPSS and KEV together is covered in the article on CVSS, EPSS and CISA KEV.
Am I affected? How to check
Installed version on the server:
nginx -vAnything below 1.30.7 (stable) or 1.31.9 (mainline) is affected, provided the respective feature is in use. Which features your nginx instance uses depends on build and configuration:
nginx -Vshows the compiled-in modules, nginx -T prints the active configuration. Depending on the flaw, HTTP/2, HTTP/3, the mail proxy module, the resolver, TLS 1.3 as well as ssi and mirror matter.
Pitfalls
Distro packages. For packages from your distribution, its patch level counts. The version number alone says little because fixes are backported. Check the package changelog.
Bundled nginx instances. Ingress controllers, panels and other products often ship their own nginx. Check their patch level separately.
Package scanners in your repo. They do not see the nginx version on your server.
What to do now
- List all nginx instances, including reverse proxies in front of other services and staging systems.
- Move to
1.30.7(stable) or1.31.9(mainline). If you run an older branch, switch to one of these two. - Afterwards verify the deployed state with
nginx -v. - For NGINX Plus, read the F5 advisories for your branch.
If you cannot patch right away
The vendor names measures only for some of the flaws, none of them replaces the update:
- CVE-2026-123634: according to the CVE record, avoid SSI and mirror directives and do not configure a proxied server name with variables.
- CVE-2026-113425: according to the CVE record, restrict listeners to trusted networks.
- CVE-2026-118899 and CVE-2026-121810: the vendor names no workaround, only the update.
- CVE-2026-123007 and CVE-2026-123633: we have no vendor statement, so we name no measure. Read the advisories on nginx.org.
Sources
- nginx.org security advisories
- CVE record CVE-2026-123634 (cveawg.mitre.org)
- CVE record CVE-2026-113425 (cveawg.mitre.org)
- CVE record CVE-2026-121810 (cveawg.mitre.org)
- CVE record CVE-2026-118899 (cveawg.mitre.org)
- CISA Known Exploited Vulnerabilities Catalog (JSON)
- Cloudflare Radar Zero Wire: nginx2root (secondary source)
Frequently asked questions
What is CVE-2026-123634?
A use-after-free in the nginx resolver, one of ten CVEs in the security release of 18 November 2026. CVSS 4.0: 9.2 CRITICAL, CVSS 3.1: 8.1 HIGH per the CVE record. The record names code execution as a possible impact if ASLR is disabled or can be bypassed.
Which versions are affected and fixed?
According to nginx.org, depending on the CVE everything from 0.5.33 to 1.31.8 is affected. Fixed are NGINX Open Source 1.31.9 (mainline) and 1.30.7 (stable). Older branches get no separate fix, there you have to move to one of these.
Is it being exploited?
Not confirmed as far as we know. The CISA assessment (SSVC) in four CVE records says "Exploitation: none", a KEV entry is not confirmed (catalog version 2026.11.17, older than the publication).
What if I cannot update right away?
For CVE-2026-123634 the vendor says: avoid SSI and mirror directives and do not configure a proxied server name with variables. For CVE-2026-113425: restrict listeners to trusted networks. For CVE-2026-118899 and CVE-2026-121810 it names no workaround, only the update.
Does the free check report this flaw?
No. The free check reads packages and runtimes from your repo, it does not see the nginx version on your server. Check it with nginx -v.