Blog
PHP flaw CVE-2026-129474: Am I affected and what to do?
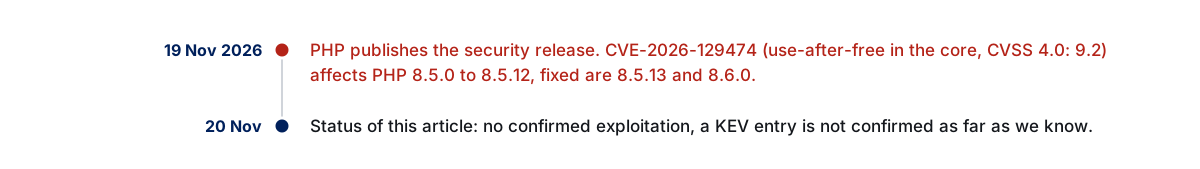
PHP published a security release on 19 November 2026. CVE-2026-129474 is a use-after-free in the core (CVSS 4.0: 9.2) and according to the advisory affects only PHP 8.5.0 to 8.5.12. Fixed are 8.5.13 and 8.6.0. Exploitation is not confirmed as far as we know. Here is how to check and what to do.
Published by Stackwatch-Team
Researched and drafted with AI assistance, reviewed and approved by the Stackwatch-Team.
What happened
The PHP project published a security release on 19 November 2026 (PHP 8.6.0, 8.5.13, 8.4.28, 8.3.37 and 8.2.36). php.net says: "The highest severity is CRITICAL." It also says: "The issues rated CRITICAL require either non-default configuration or uncommon setups." This is PHP's own rating, not a CVSS value.
This article evaluates one flaw:
- CVE-2026-129474 (GHSA-8mjj-2r7p-4hg2): "Use-after-free in magic method backtraces can lead to remote code execution". Weakness type CWE-416. CVSS 4.0: 9.2, severity "Critical", vector
CVSS:4.0/AV:N/AC:H/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N. The source is the php-src project's advisory on GitHub, not the NVD.
The release contains further fixes, including changelog entries for Date and Session with "can lead to remote code execution" in the title (among them CVE-2026-129496 and CVE-2026-126714). We have no CVSS value and no affected-version statement for these, so we do not evaluate them here.
Affected and fixed versions
According to the GitHub advisory, only the range >= 8.5.0, < 8.5.13 is affected. Fixed is 8.5.13, and 8.6.0 according to the changelog.
| Branch | Affected | Fixed in |
|---|---|---|
| PHP 8.6 | the advisory names no affected range | 8.6.0 |
| PHP 8.5 | 8.5.0 to 8.5.12 | 8.5.13 |
| PHP 8.4 | not affected (outside the range according to the advisory) | – |
| PHP 8.3 | not affected (outside the range according to the advisory) | – |
| PHP 8.2 | not affected (outside the range according to the advisory) | – |
This matches the changelog: CVE-2026-129474 appears only under 8.6.0 and 8.5.13. According to php.net, support for PHP 8.2 ends on 31 December 2026. How to spot runtimes without support is covered in the end-of-life overview.
Is it being exploited?
As far as we know: no confirmed exploitation.
- The GitHub advisory names no exploitation.
- CISA's Known Exploited Vulnerabilities catalog (KEV) does not list CVE-2026-129474 as far as we know. The catalog version we checked (2026.11.18) is older than the publication on 19 November, and we did not read the whole file.
- The vector contains
AC:HandAT:P: according to CVSS the attack is not trivial and has prerequisites. The advisory details we have do not say which ones.
This can change. How to read CVSS, EPSS and KEV together is covered in the article on CVSS, EPSS and CISA KEV.
Am I affected? How to check
Installed version on the server:
php -vIf you use PHP-FPM:
php-fpm -vOnly 8.5.0 to 8.5.12 is affected. In containers, check the image, not the host:
docker run --rm <image> php -vRunning containers keep the old version until you restart them.
Pitfalls
Distro packages. For packages from Debian, Ubuntu, RHEL, Remi or Sury, the distribution's patch level counts. The version number alone says little because fixes are backported.
Docker. Pull php:8.5 images again and rebuild your images.
Running workers. Restart PHP-FPM and Apache mod_php after the update, running workers use the old binary.
Changing only the CLI configuration. According to the advisory this is not sufficient as a mitigation (see below).
Package scanners in your repo. They do not see the PHP runtime on your server.
What to do now
- List all PHP instances, including staging systems and containers.
- Only
8.5.xmatters: if you run8.5.0to8.5.12, move to8.5.13or8.6.0. - Restart PHP-FPM or Apache and redeploy containers.
- Afterwards verify the deployed state with
php -v.
If you cannot patch right away
In the GitHub advisory the vendor names as the measure: upgrade to PHP 8.5.13. As an immediate measure it says to set zend.exception_ignore_args=1 in the configuration used by the affected PHP workers and restart them. According to the advisory, fatal_error_backtraces=0 also prevents this attack path.
Two limits from the advisory:
- Changing the configuration only for the CLI is not sufficient.
display_errors=0does not prevent PHP from building the backtrace.
The fix remains the update.
Sources
Frequently asked questions
What is CVE-2026-129474?
A use-after-free in magic method backtraces in the PHP core that can lead to remote code execution according to the GitHub advisory. CVSS 4.0: 9.2 (Critical), with prerequisites (AC:H, AT:P). Published on 19 November 2026.
Which PHP versions are affected and fixed?
According to the advisory only PHP 8.5.0 to 8.5.12 is affected. Fixed are 8.5.13 and 8.6.0. PHP 8.2 to 8.4 are outside the affected range according to the advisory.
Is it being exploited?
Not confirmed as far as we know. The advisory names no exploitation, a KEV entry is not confirmed (catalog version 2026.11.18, older than the publication).
What if I cannot update right away?
As an immediate measure the vendor says to set zend.exception_ignore_args=1 in the configuration of the affected PHP workers and restart them. fatal_error_backtraces=0 also prevents this attack path. Changing only the CLI configuration is not sufficient. The fix remains the update.
Does the free check report this flaw?
No. The free check reads packages and runtimes from your repo, it does not see the PHP version on your server. Check it with php -v.