Blog
TYPO3 flaw CVE-2026-119623: Am I affected and what to do?
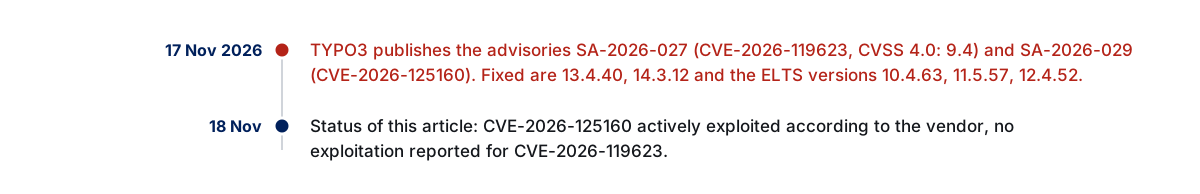
The TYPO3 installer lacks sufficient authentication, which according to the advisory leads to remote code execution (CVSS 9.4). Fixed are 13.4.40 and 14.3.12 as well as the ELTS versions 10.4.63, 11.5.57 and 12.4.52. The same wave contains a Form Framework flaw that the vendor says is actively exploited. Here is how to check and what to do.
Published by Stackwatch-Team
Researched and drafted with AI assistance, reviewed and approved by the Stackwatch-Team.
What happened
The TYPO3 project published several core security advisories on 17 November 2026. Two of them matter here:
- CVE-2026-119623 (TYPO3-CORE-SA-2026-027, CWE-306, "Missing Authentication in Installer"): the installer can be used without sufficient authentication. According to the advisory this leads to remote code execution. The advisory also says a backend user with low privileges can create the marker file that unlocks the installer. CVSS 4.0: 9.4 CRITICAL (
CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H) per the CVE record, the "Suggested CVSS" in the advisory is identical. - CVE-2026-125160 (TYPO3-CORE-SA-2026-029, "Information Disclosure in Form Framework"): when saving a form fails, the upload subfolder becomes visible and attackers can reach uploaded files. This matters mostly where forms accept uploads. CVSS 4.0: 6.3 MEDIUM per the TYPO3 advisory.
The same release wave contains further advisories, for example TYPO3-CORE-SA-2026-028. They are not evaluated here, read them at the vendor if in doubt.
Affected and fixed versions
Both CVEs affect the same version ranges:
| Branch | Affected | Fixed in |
|---|---|---|
| TYPO3 14.x | 14.0.0 to 14.3.11 | 14.3.12 (LTS) |
| TYPO3 13.x | 13.0.0 to 13.4.39 | 13.4.40 (LTS) |
| TYPO3 12.x | 12.0.0 to 12.4.51 | 12.4.52 (ELTS) |
| TYPO3 11.x | 11.0.0 to 11.5.56 | 11.5.57 (ELTS) |
| TYPO3 10.x | 10.0.0 to 10.4.62 | 10.4.63 (ELTS) |
ELTS stands for Extended Long Term Support, the vendor's extended support offering. The advisory lists the fixes for 10.4, 11.5 and 12.4 only as ELTS versions. The advisories say nothing about branches below 10.x, so neither do we.
Is it being exploited?
CVE-2026-125160 (Form Framework): yes, according to the vendor. The advisory and the CVE record state: "This vulnerability is known to be actively exploited." Against that stands the CISA assessment in the CVE record (SSVC), which says "Exploitation: none". We cannot resolve the contradiction. We take the vendor's statement seriously. As far as we know the CVE is not in CISA's Known Exploited Vulnerabilities (KEV) catalog, but the catalog version we checked (2026.11.13) is older than the publication on 17 November.
CVE-2026-119623 (installer): the advisory and the CVE record name no exploitation. The CISA assessment in the CVE record reads "Exploitation: none", "Automatable: no", "Technical Impact: total". It is not reported as actively exploited. The risk is still high: if an attack succeeds, the impact is total according to the CISA assessment.
How to read CVSS, EPSS and KEV together is explained in the article on CVSS, EPSS and CISA KEV.
Am I affected? How to check
Installed core version in a Composer installation:
composer show typo3/cms-coreIn the lockfile:
grep -A2 '"name": "typo3/cms-core"' composer.lockPlus the advisory's hint on the installer: check the web root and the project root for unexpected files whose name starts with FIRST_INSTALL:
find . -maxdepth 2 -name 'FIRST_INSTALL*'Also check the backend for admins and system maintainers you do not recognise.
Pitfalls
Composer installations. After updating with composer update typo3/cms-core, clear the cache.
Docker images. Rebuild images with an old build state, otherwise the old core keeps running.
Nginx. The bundled fileadmin/.htaccess only works on Apache. On Nginx you have to configure the protection for the upload folder yourself.
Manual configuration. According to advisory TYPO3-CORE-SA-2026-028, manual configuration may be needed after the update, for example for image formats such as psd or ppm in $GLOBALS['TYPO3_CONF_VARS']['SYS']['FileInfo']['fileExtensionToMimeType']. Read the advisory before you deploy to production.
What to do now
- List all TYPO3 installations, including rarely deployed ones and staging systems.
- Raise the core to
13.4.40or14.3.12. For 10.4, 11.5 and 12.4 the fix is available as the ELTS versions10.4.63,11.5.57and12.4.52. - Clear the cache, rebuild images, deploy.
- Verify with
composer show typo3/cms-coreon the deployed system. - Check for
FIRST_INSTALL*files and unknown backend admins. If you find anything unusual, assume a compromise.
If you cannot patch right away
The vendor names measures that do not replace the update:
- CVE-2026-125160: according to the advisory, files in the form upload target folder should be delivered with a restrictive Content-Security-Policy. On Apache the
fileadmin/.htaccesscovers this, other web servers such as Nginx have to be configured manually. - CVE-2026-119623: check the web root and the project root for unexpected
FIRST_INSTALL*files, and check backend admins and system maintainers for unknown entries.
In both cases the fix remains the update.
Sources
Frequently asked questions
What is CVE-2026-119623?
Missing authentication in the TYPO3 installer (CWE-306, TYPO3-CORE-SA-2026-027), which according to the advisory leads to remote code execution. CVSS 4.0: 9.4 CRITICAL per the CVE record.
Which versions are affected and fixed?
Affected are TYPO3 10.0.0 to 10.4.62, 11.0.0 to 11.5.56, 12.0.0 to 12.4.51, 13.0.0 to 13.4.39 and 14.0.0 to 14.3.11. Fixed are 10.4.63, 11.5.57 and 12.4.52 (each ELTS) as well as 13.4.40 and 14.3.12 (LTS).
Is it being exploited?
For CVE-2026-119623 the advisory and the CVE record name no exploitation. For CVE-2026-125160 in the Form Framework the vendor writes "known to be actively exploited", while the CISA assessment in the CVE record says "Exploitation: none". A KEV entry is not confirmed as far as we know (catalog version 2026.11.13, older than the publication).
What if I cannot update right away?
The vendor names checks but no substitute for the update: check the web root and project root for FIRST_INSTALL* files, check backend admins for unknown entries, deliver form upload folders with a restrictive Content-Security-Policy.
Does the free check report this flaw?
It reads package versions from your repo’s lockfile, for Composer projects that is typo3/cms-core in composer.lock. It does not check whether a FIRST_INSTALL file sits on the server: you have to check that there yourself.