Blog
React flaw CVE-2026-126187: Am I affected and what to do?
In React Server Components, a server response with several typed arrays plus an attacker-controlled value can lead to unauthenticated remote code execution, according to the CVE only in extremely rare cases. Fixed are react-server-dom-* 19.0.9, 19.1.10, 19.2.9 and 19.3.1, and Next.js 16.4.1. Here is how to check and what to do.
Published by Stackwatch-Team
Researched and drafted with AI assistance, reviewed and approved by the Stackwatch-Team.
What happened
React Server Components contain a flaw that can lead to unauthenticated remote code execution: CVE-2026-126187 (CWE-502, deserialization of untrusted data). According to the CVE description it applies when a server response carries several typed arrays plus an attacker-controlled value, and only in "extremely rare cases".
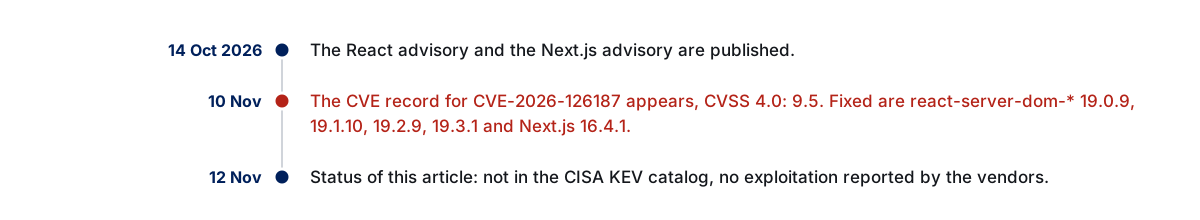
CVSS 4.0: 9.5 CRITICAL (CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:N), assigned by GitHub as CNA in the CVE record. The React advisory GHSA-xqc2-xf4c-x3h3 and the Next.js advisory GHSA-673q-mjm6-r5xr give the same vector. The CVE record was published on 10 November 2026, both advisories are dated 14 October 2026.
According to the CVE record, the ID belongs to the React packages react-server-dom-*. The Next.js advisory lists "No known CVE". That both describe the same flaw is stated only by Cloudflare Zero Wire, not by the vendor.
Affected and fixed versions
| Package | Affected | Fixed in |
|---|---|---|
react-server-dom-webpack, -parcel, -turbopack (19.0) | from 19.0.0, before 19.0.9 | 19.0.9 |
react-server-dom-webpack, -parcel, -turbopack (19.1) | from 19.1.0, before 19.1.10 | 19.1.10 |
react-server-dom-webpack, -parcel, -turbopack (19.2) | from 19.2.0, before 19.2.9 | 19.2.9 |
react-server-dom-webpack, -parcel, -turbopack (19.3) | from 19.3.0, before 19.3.1 | 19.3.1 |
Next.js (next) 16.x | 16.0.0 to 16.4.0, only with use cache functions returning several typed arrays | 16.4.1 |
According to the CVE record, applications without a server part in React, and applications without a framework or bundler that supports React Server Components, are not affected.
For Next.js 15.x and for branches outside the table (for example React below 19.0.0) the CVE record and the advisories say nothing. We therefore say nothing either. Check the advisories directly if you are on one of those.
Is it being exploited?
There is no statement from the vendors. The CVE record lists "discovery: UNKNOWN", and both GitHub advisories mention no exploitation. As of 12 November 2026, CISA does not list CVE-2026-126187 in its Known Exploited Vulnerabilities (KEV) catalog. The catalog version we checked (2026.11.10) is older than the CVE record, so an entry was not yet possible. According to Cloudflare Zero Wire (secondary, not confirmed by the vendor), no exploitation had been reported by 11 November. How to read CVSS, EPSS and KEV together is explained in the article on CVSS, EPSS and CISA KEV.
Am I affected? How to check
Installed versions in your project:
npm ls react-server-dom-webpack react-server-dom-parcel react-server-dom-turbopack nextIn the lockfile:
grep -E '"(next|react-server-dom-[a-z]+)"' package-lock.jsonWith Next.js the code matters too: according to the advisory, only applications with use cache functions that return several typed arrays (Uint8Array and relatives) are affected. Search your code for them.
Pitfalls
Update Next.js separately. According to Cloudflare (secondary, not confirmed by the vendor), updating React alone does not fix the flaw in Next.js. Raise next itself to 16.4.1.
Package scanners only see the lockfile. They detect the version, but not whether your application uses use cache with typed arrays.
Docker images. Rebuild images with an old build state, do not just change the code.
Restart. After deploying, restart servers and workers so the old code does not keep running.
What to do now
- List projects with React Server Components or Next.js, including rarely deployed ones.
- Raise
react-server-dom-*to19.0.9,19.1.10,19.2.9or19.3.1, depending on the branch. - With Next.js 16.x, raise
nextto16.4.1. - Regenerate the lockfile, rebuild images, deploy and restart servers.
- Verify with
npm lson the deployed state.
If you cannot patch right away
The vendor names no workaround, only the update. The React advisory recommends updating immediately. The Next.js advisory says there is no known workaround for affected applications with such use cache functions and advises upgrading immediately, even if your application has no similar functions. We therefore publish no configuration rules.
Sources
Frequently asked questions
What is CVE-2026-126187?
A deserialization flaw (CWE-502) in React Server Components that can lead to unauthenticated remote code execution, according to the CVE description only in extremely rare cases. CVSS 4.0: 9.5 CRITICAL according to GitHub as CNA in the CVE record.
Which versions are affected and fixed?
Affected are react-server-dom-webpack, -parcel and -turbopack from 19.0.0 before 19.0.9, from 19.1.0 before 19.1.10, from 19.2.0 before 19.2.9, and 19.3.0. Fixed are 19.0.9, 19.1.10, 19.2.9 and 19.3.1. With Next.js 16.x, 16.0.0 to 16.4.0 are affected (only with use cache functions returning several typed arrays), 16.4.1 is fixed.
Is it being exploited?
No primary source mentions exploitation. As of 12 November 2026 the flaw is not in the CISA KEV catalog (catalog version 2026.11.10, older than the CVE record). According to Cloudflare Zero Wire (secondary), no exploitation had been reported by 11 November.
What if I cannot update right away?
The vendor names no workaround, only the update. Both advisories advise updating immediately.
Does the free check report this flaw?
It reads the versions of next and react-server-dom-* from the lockfile of your repo and shows whether an affected version is in there. It does not check whether your code uses use cache with typed arrays: search for that yourself.