Blog
WordPress flaw CVE-2026-119977: Am I affected and what to do?
While a WordPress core update is being unpacked, an unauthenticated attacker can hit the briefly visible staging path and execute code. Core 4.7 to 7.1.3 is affected, 7.1.4 is fixed, and older branches get backports. The flaw is in the CISA KEV catalog. Here is how to check and what to do.
Published by Stackwatch-Team
Researched and drafted with AI assistance, reviewed and approved by the Stackwatch-Team.
What happened
While WordPress unpacks a core update, the new files sit for a few seconds in a staging folder under wp-content/upgrade/. With CVE-2026-119977 (CWE-367, race condition between check and use) an unauthenticated attacker can hit that path during the short window and execute code. WordPress's advisory carries the ID GHSA-4w3m-c66w-69mg.
CVSS 3.1: 8.1 (AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:H/A:H), assigned by Wordfence as CNA in the CVE record. WordPress's GitHub advisory rates the same flaw "Low" and lists "No known CVE". That contradiction is open. The attack is complex (AC:H): it needs exactly the update window.
Affected and fixed versions
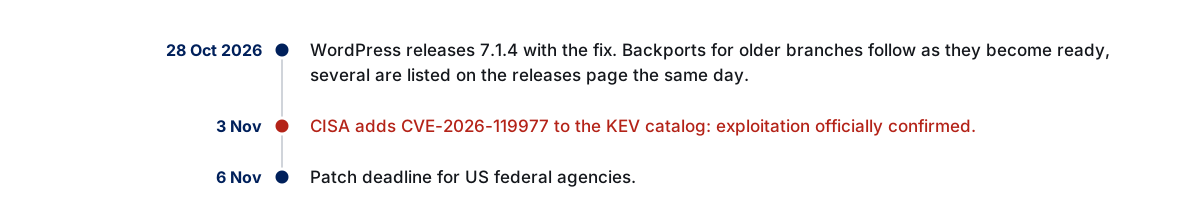
WordPress core from 4.7 to 7.1.3 is affected (per the CVE record and the advisory). The fix is in 7.1.4 (released 28 October 2026). Older branches get backports. The advisory lists them, and the releases page shows several of them dated 28 October 2026.
| Branch | Affected | Fixed in |
|---|---|---|
| WordPress 7.1 | 7.1.0 to 7.1.3 | 7.1.4 |
| WordPress 7.0 | 7.0.0 to 7.0.7 | 7.0.8 |
| WordPress 6.9 | 6.9.0 to 6.9.10 | 6.9.11 |
| WordPress 6.8 | all versions before a fix | 6.8.12 |
| WordPress 6.7 | all versions before a fix | 6.7.11 |
| WordPress 6.6 | all versions before a fix | 6.6.11 |
| WordPress 6.5 | all versions before a fix | 6.5.14 |
| WordPress 6.4 | all versions before a fix | 6.4.14 |
| WordPress 6.3 | all versions before a fix | 6.3.14 |
| WordPress 6.2 | all versions before a fix | 6.2.15 |
| WordPress 6.1 | all versions before a fix | 6.1.16 |
| WordPress 6.0 to 4.7 | all versions before a fix | per branch in the advisory, last 4.7.39 |
The sources disagree on the backports: the 28 October release post says the backports are "in progress" and ship as they become ready. The advisory says the fix has been "backported to all branches back to 4.7". The download page of your branch on wordpress.org is authoritative. Which versions still get updates at all is covered in the end-of-life overview.
Is it being exploited?
Yes, according to CISA. On 3 November 2026 the agency added CVE-2026-119977 to its Known Exploited Vulnerabilities (KEV) catalog, with a deadline of 6 November 2026 for US federal agencies. There is no solid primary source on the scale or number of attacks, so we quote no numbers. How to read CVSS, EPSS and KEV together is covered in CVSS, EPSS and CISA KEV.
Am I affected? How to check
Installed version (WP-CLI in the web root):
wp core versionWithout WP-CLI:
grep '$wp_version =' wp-includes/version.phpThe staging folder should be empty. Leftovers point to an aborted or running update:
ls -la wp-content/upgrade/
find wp-content/upgrade -name '*.php'
Requests to the path in your logs (nginx shown, adjust the path):
grep 'wp-content/upgrade/' /var/log/nginx/access.logPitfalls
Docker images and managed hosting. Check the state of the image or host, not just the dashboard.
Composer setups. With roots/wordpress and similar setups the version comes from composer.json, not from the dashboard.
Package scanners do not see the window. It is behavior of the updater, not a vulnerable package in a lockfile.
What to do now
- Check the version (
wp core version). - Update to
7.1.4, on older branches to the fixed version of your branch (table above, check the state on wordpress.org). - Afterwards run
wp core versionon the live system and checkwp-content/upgrade/for leftovers. - Search the logs for requests to
/wp-content/upgrade/, especially since 28 October. - If you find hits, treat the site as compromised: compare files with a clean install, review administrator accounts and passwords.
If you cannot patch right away
The vendor names no workaround, only the update. We therefore publish no configuration rules. If you are stuck on a branch without a released backport, watch the download page of your branch and check the logs for requests to /wp-content/upgrade/.
Sources
Frequently asked questions
What is CVE-2026-119977?
A race condition (CWE-367) in the WordPress core update process. For a few seconds the staging path wp-content/upgrade/ is reachable, and an unauthenticated attacker can execute code through it. CVSS 3.1: 8.1 according to Wordfence as CNA in the CVE record. The GitHub advisory of WordPress says "Low"; that contradiction is open.
Which versions are affected and fixed?
WordPress core 4.7 to 7.1.3 is affected. 7.1.4 (28 October 2026) is fixed. For older branches the advisory lists backports, for example 7.0.8, 6.9.11 and 6.8.12, down to 4.7.39. The download page of your branch is authoritative.
Is it being exploited?
Yes, according to CISA: the flaw has been in the KEV catalog since 3 November 2026, with a deadline of 6 November for US federal agencies. We quote no attack numbers; there is no solid primary source for them.
What if I cannot update right away?
The vendor names no workaround, only the update. Until then, watch the logs for requests to /wp-content/upgrade/.
Does the free check report this flaw?
No. The free check reads packages and runtimes from the repo; WordPress core is not part of it. Check the version with wp core version.